Flask Production-Ready Auth System — From Messy Login Screens to Bulletproof APIs
"I spent hours building a Flask auth system, only to realize it had security holes big enough to drive a truck through!"
If that sounds familiar, you're not alone. Many developers (myself included) learn the hard way that slapping together a quick /login endpoint isn’t enough for production. Between shaky error handling, messy file structures, and overlooked security risks, auth systems can quickly become a nightmare.
What if you could build a Flask auth API that’s:
✔ Secure (password hashing, JWT best practices, rate limiting)
✔ Well-structured (clean, scalable folder setup)
✔ Production-ready (proper error handling, logging, and docs)
Let’s build it—step by step—with explanations for every file and decision.
📂 Folder Structure (Scalable from Day 1)
Here’s the structure we’ll use (and why):
/flask_auth_project
│
├── /app
│   ├── __init__.py          # Flask app factory
│   ├── extensions.py        # DB, JWT, etc. initialization
│   ├── config.py            # Config classes (Dev/Prod/Test)
│   │
│   ├── /auth                # Auth blueprint
│   │   ├── __init__.py
│   │   ├── models.py        # User model
│   │   ├── routes.py        # Login, register, logout routes
│   │   ├── schemas.py       # Marshmallow validation
│   │   └── utils.py         # Password hashing, token helpers
│   │
│   ├── /middleware          # Custom middleware
│   │   └── auth_middleware.py  # JWT validation
│   │
│   ├── /static/docs         # API docs (Swagger/Postman)
│   └── /tests              # Tests (pytest)
│
├── requirements.txt         # Dependencies
├── .env.example             # Env variable template
└── run.py                   # Entry point
Why this structure?
- Separation of concerns: Auth logic isn’t tangled with other features.
- Easy testing: Isolated auth blueprint and dedicated
/tests. - Scalable: Add more blueprints (e.g.,
/posts,/billing) without chaos.
🔐 Core Authentication Files (Explained)
1. app/extensions.py – Safely Initialize Tools
from flask_sqlalchemy import SQLAlchemy
from flask_jwt_extended import JWTManager

db = SQLAlchemy()
jwt = JWTManager()

# Optional: JWT claims for role-based access
@jwt.additional_claims_loader
def add_claims_to_jwt(identity):
    return {"is_admin": False}  # Customize per user
Key Notes:
- Keep extensions in one place to avoid circular imports.
- Use
flask_jwt_extended(notflask_jwt)—it supports refresh tokens and better security.
2. app/auth/models.py – The User Model
from app.extensions import db
from werkzeug.security import generate_password_hash, check_password_hash

class User(db.Model):
    id = db.Column(db.Integer, primary_key=True)
    email = db.Column(db.String(80), unique=True, nullable=False)
    password_hash = db.Column(db.String(128))

    def set_password(self, password):
        self.password_hash = generate_password_hash(password)

    def check_password(self, password):
        return check_password_hash(self.password_hash, password)
Security Tip:
- Never store plain-text passwords (
generate_password_hashuses PBKDF2 by default). - Add fields like
is_verified,last_login_atfor production.
3. app/auth/schemas.py – Request Validation
from marshmallow import Schema, fields, validate

class UserSchema(Schema):
    email = fields.Email(required=True)
    password = fields.Str(required=True, validate=validate.Length(min=8))

class LoginSchema(UserSchema):
    pass  # Reuse validation for consistent rules
Why Marshmallow?
- Validate input before it hits your routes (e.g., enforce strong passwords).
- Returns user-friendly errors (e.g.,
"Email is invalid").
4. app/auth/routes.py – Secure Endpoints
from flask import request, jsonify
from flask_jwt_extended import create_access_token
from app.auth.models import User
from app.auth.schemas import LoginSchema

@auth_bp.route('/register', methods=['POST'])
def register():
    data = LoginSchema().load(request.get_json())  # Validates input
    if User.query.filter_by(email=data['email']).first():
        return {"error": "Email already exists"}, 409

    user = User(email=data['email'])
    user.set_password(data['password'])
    db.session.add(user)
    db.session.commit()

    return jsonify({"msg": "User created"}), 201

@auth_bp.route('/login', methods=['POST'])
def login():
    data = LoginSchema().load(request.get_json())
    user = User.query.filter_by(email=data['email']).first()

    if not user or not user.check_password(data['password']):
        return {"error": "Invalid credentials"}, 401

    access_token = create_access_token(identity=user.id)
    return jsonify(access_token=access_token)
Critical Details:
- HTTP Status Codes:
401for auth failures,409for conflicts. - JWT Tokens: Set short expiration times (e.g., 15 mins) and use refresh tokens.
🛡️ Security Upgrades (Production Must-Haves)
1. Rate Limiting (Prevent Brute Force)
Add in app/extensions.py:
from flask_limiter import Limiter
from flask_limiter.util import get_remote_address

limiter = Limiter(key_func=get_remote_address, default_limits=["200 per day", "50 per hour"])
Then protect login:
@auth_bp.route('/login', methods=['POST'])
@limiter.limit("5 per minute")
def login():
    ...
2. HTTPS & JWT Hardening
In config.py:
class ProdConfig:
    JWT_COOKIE_SECURE = True  # Only send over HTTPS
    JWT_ACCESS_TOKEN_EXPIRES = timedelta(minutes=15)
3. Logging
Log failed logins (add to login() route):
import logging
logging.warning(f"Failed login attempt for {data['email']}")
💡 FAQ (Common Gotchas)
Q: Should I use sessions or JWTs?
A: JWTs for APIs (stateless), sessions for server-rendered apps.
Q: How do I handle password resets?
A: Generate a time-limited token, store its hash in the DB, and email a link.
Q: Why not just use Flask-Login?
A: Flask-Login is great for sessions but less flexible for APIs.
🚀 Your Turn!
Try adding:
- Email verification (with Flask-Mail)
- Role-based access control (add
user.roleto JWT claims)
What’s your #1 auth struggle? Let me know in the comments! 👇
Projects to explore next
Source-code projects from the KritiMyantra catalogue. Check each project's details before buying.
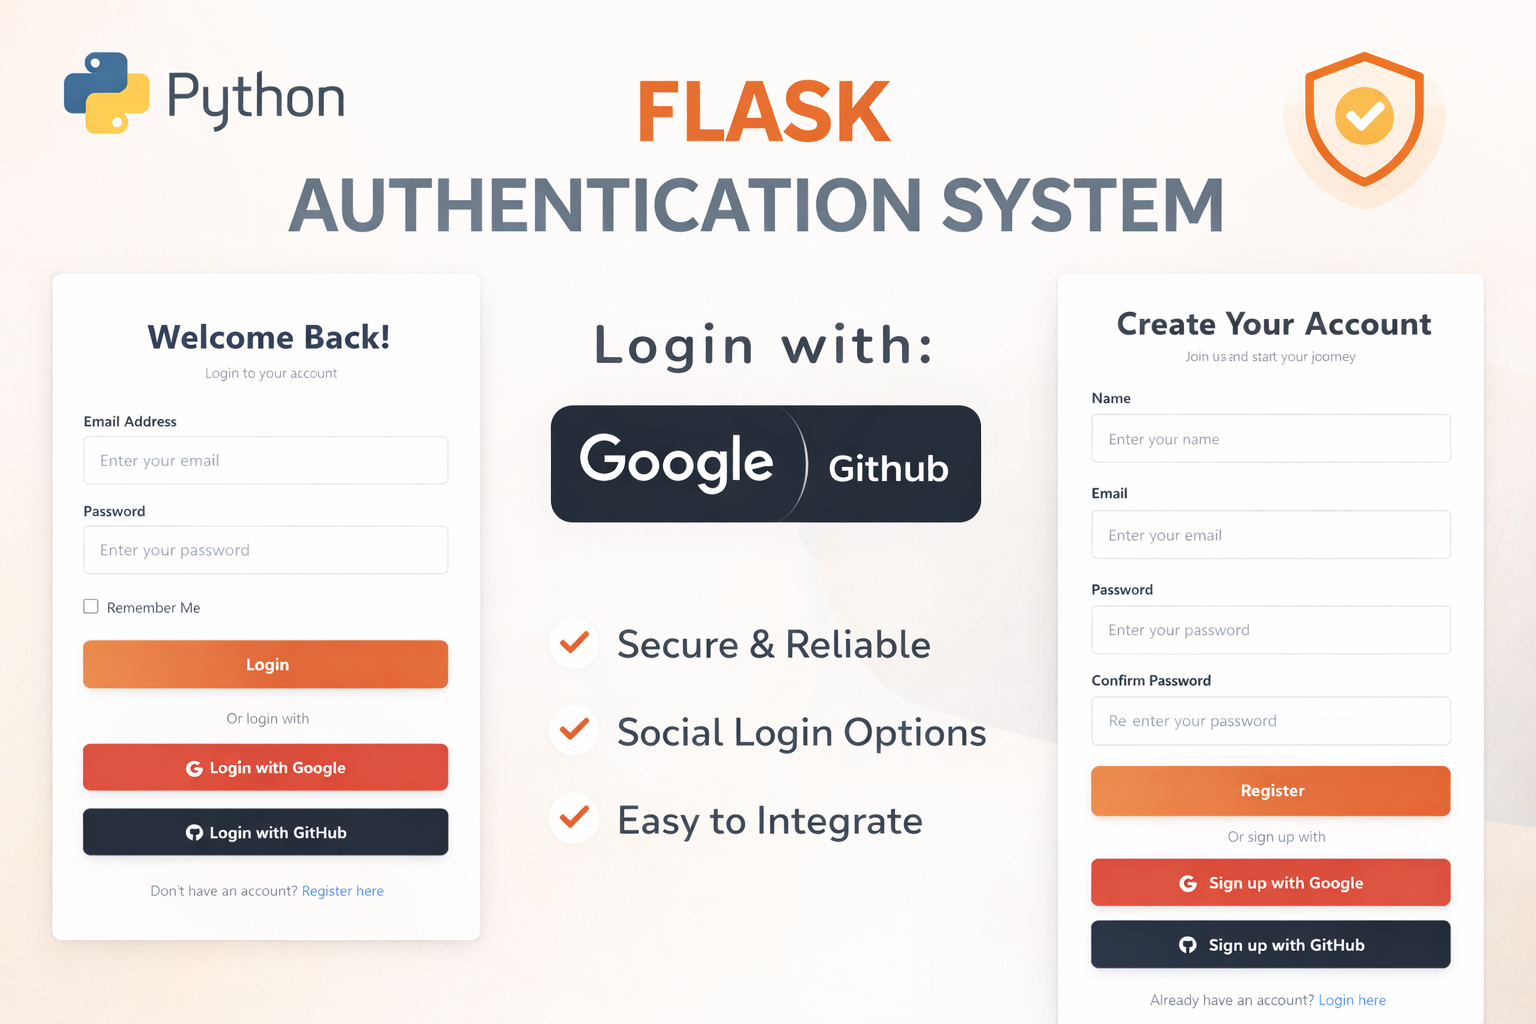
Flask Authentication System (Free Version) - Kritim Yantra
🛠 Features✔ Google & GitHub Authentication✔ User Registration & Login✔ Profile/Dashboard Access✔ Secure & Mi...
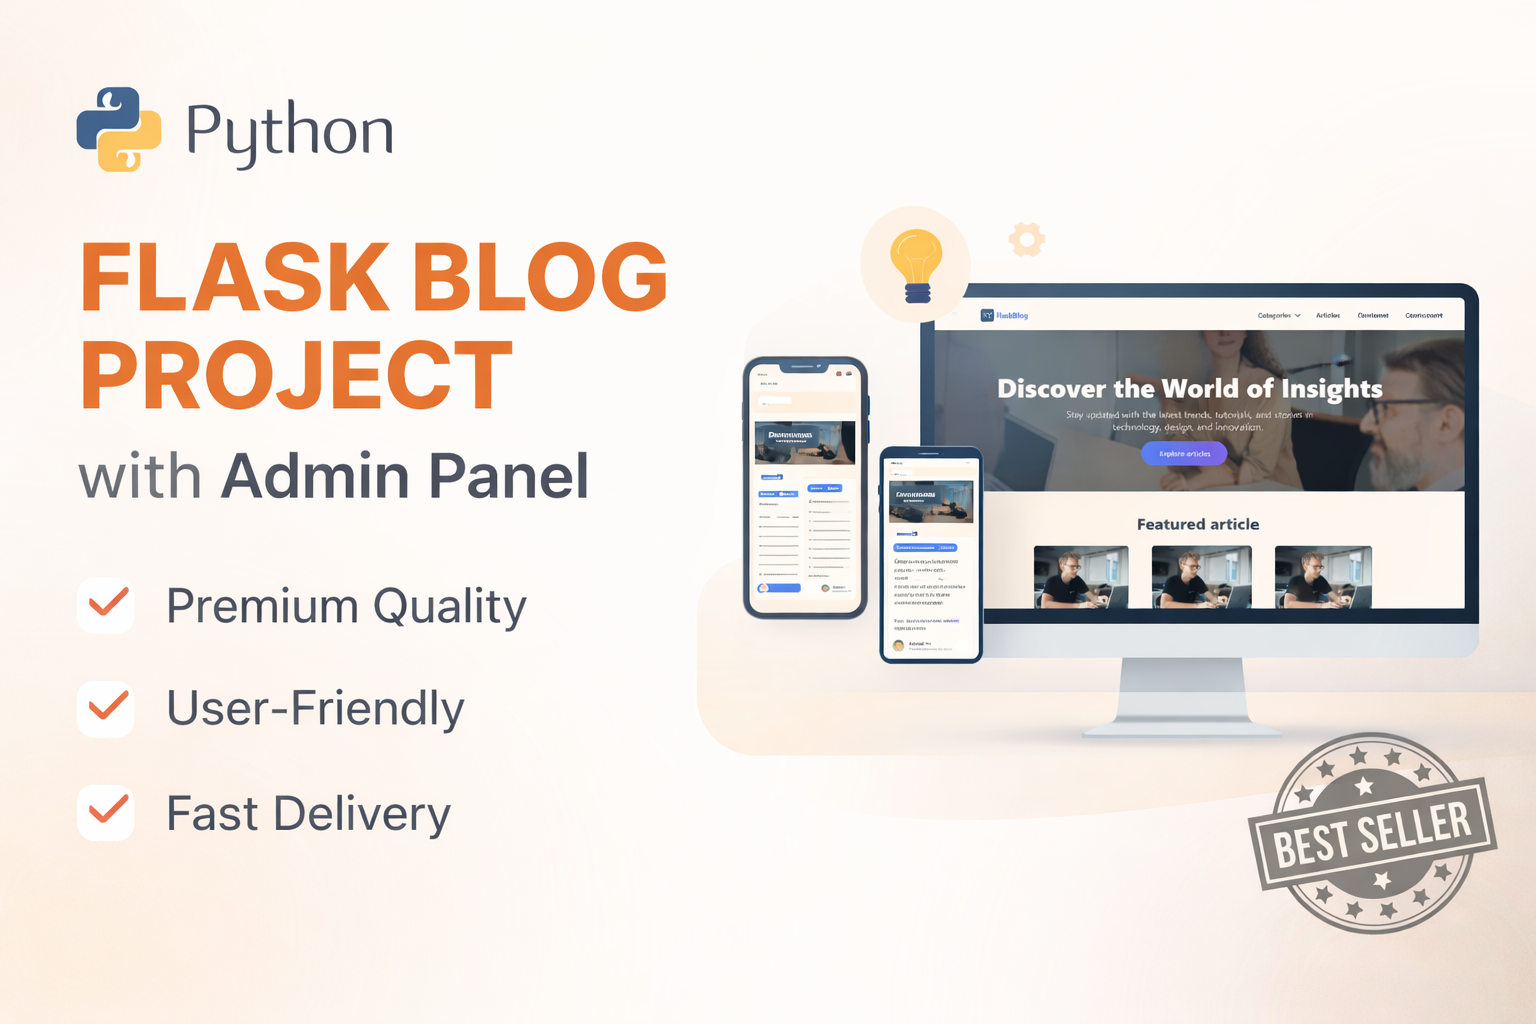
Flask Blog CMS with Admin Dashboard — Python Source Code
A Flask-based blogging website with a built-in admin dashboard. Manage articles, images, categories, tags and featured p...
Laravel 12 + ReactJS Starter Kit: Add Multi-Language Support (Arabic, English, Spanish) with Blog CRUD
🚀 Installation & Setup Download & Extract Get the ZIP from kritimyantra.com and extract it. Includes preconfigu...
How to Upload Images in Laravel 12: A Step-by-Step Guide
Welcome to this comprehensive guide on uploading images in Laravel 12! Whether you're building a blog, an e-commerce si...
Python sync Function: A Complete Guide
Python, being a powerful and flexible language, supports both synchronous and asynchronous programming models. In this post, we'll...
Making Asynchronous HTTP Requests in Python with aiohttp
When working with APIs or scraping web pages, the traditional requests library blocks your program until a response is received. B...
Comments
No comments yet. Be the first to comment.
Sign in to join the discussion.